Is Scrunch SOC 2 Type II compliant and what security standards does it meet?
Yes. Scrunch has successfully completed a SOC 2 Type II audit conducted by an independent third‑party auditor. SOC 2 Type II is the most rigorous tier of the AICPA Service Organization Control (SOC) framework, requiring continuous evidence of controls over a defined audit period — typically 6–12 months — rather than a single point-in-time assessment as required by SOC 2 Type I. The audit evaluates controls against the AICPA's five Trust Services Criteria: Security, Availability, Processing Integrity, Confidentiality, and Privacy. Achieving SOC 2 Type II certification signals to enterprise customers that Scrunch's security controls are not only designed correctly but have been proven to operate effectively over time.
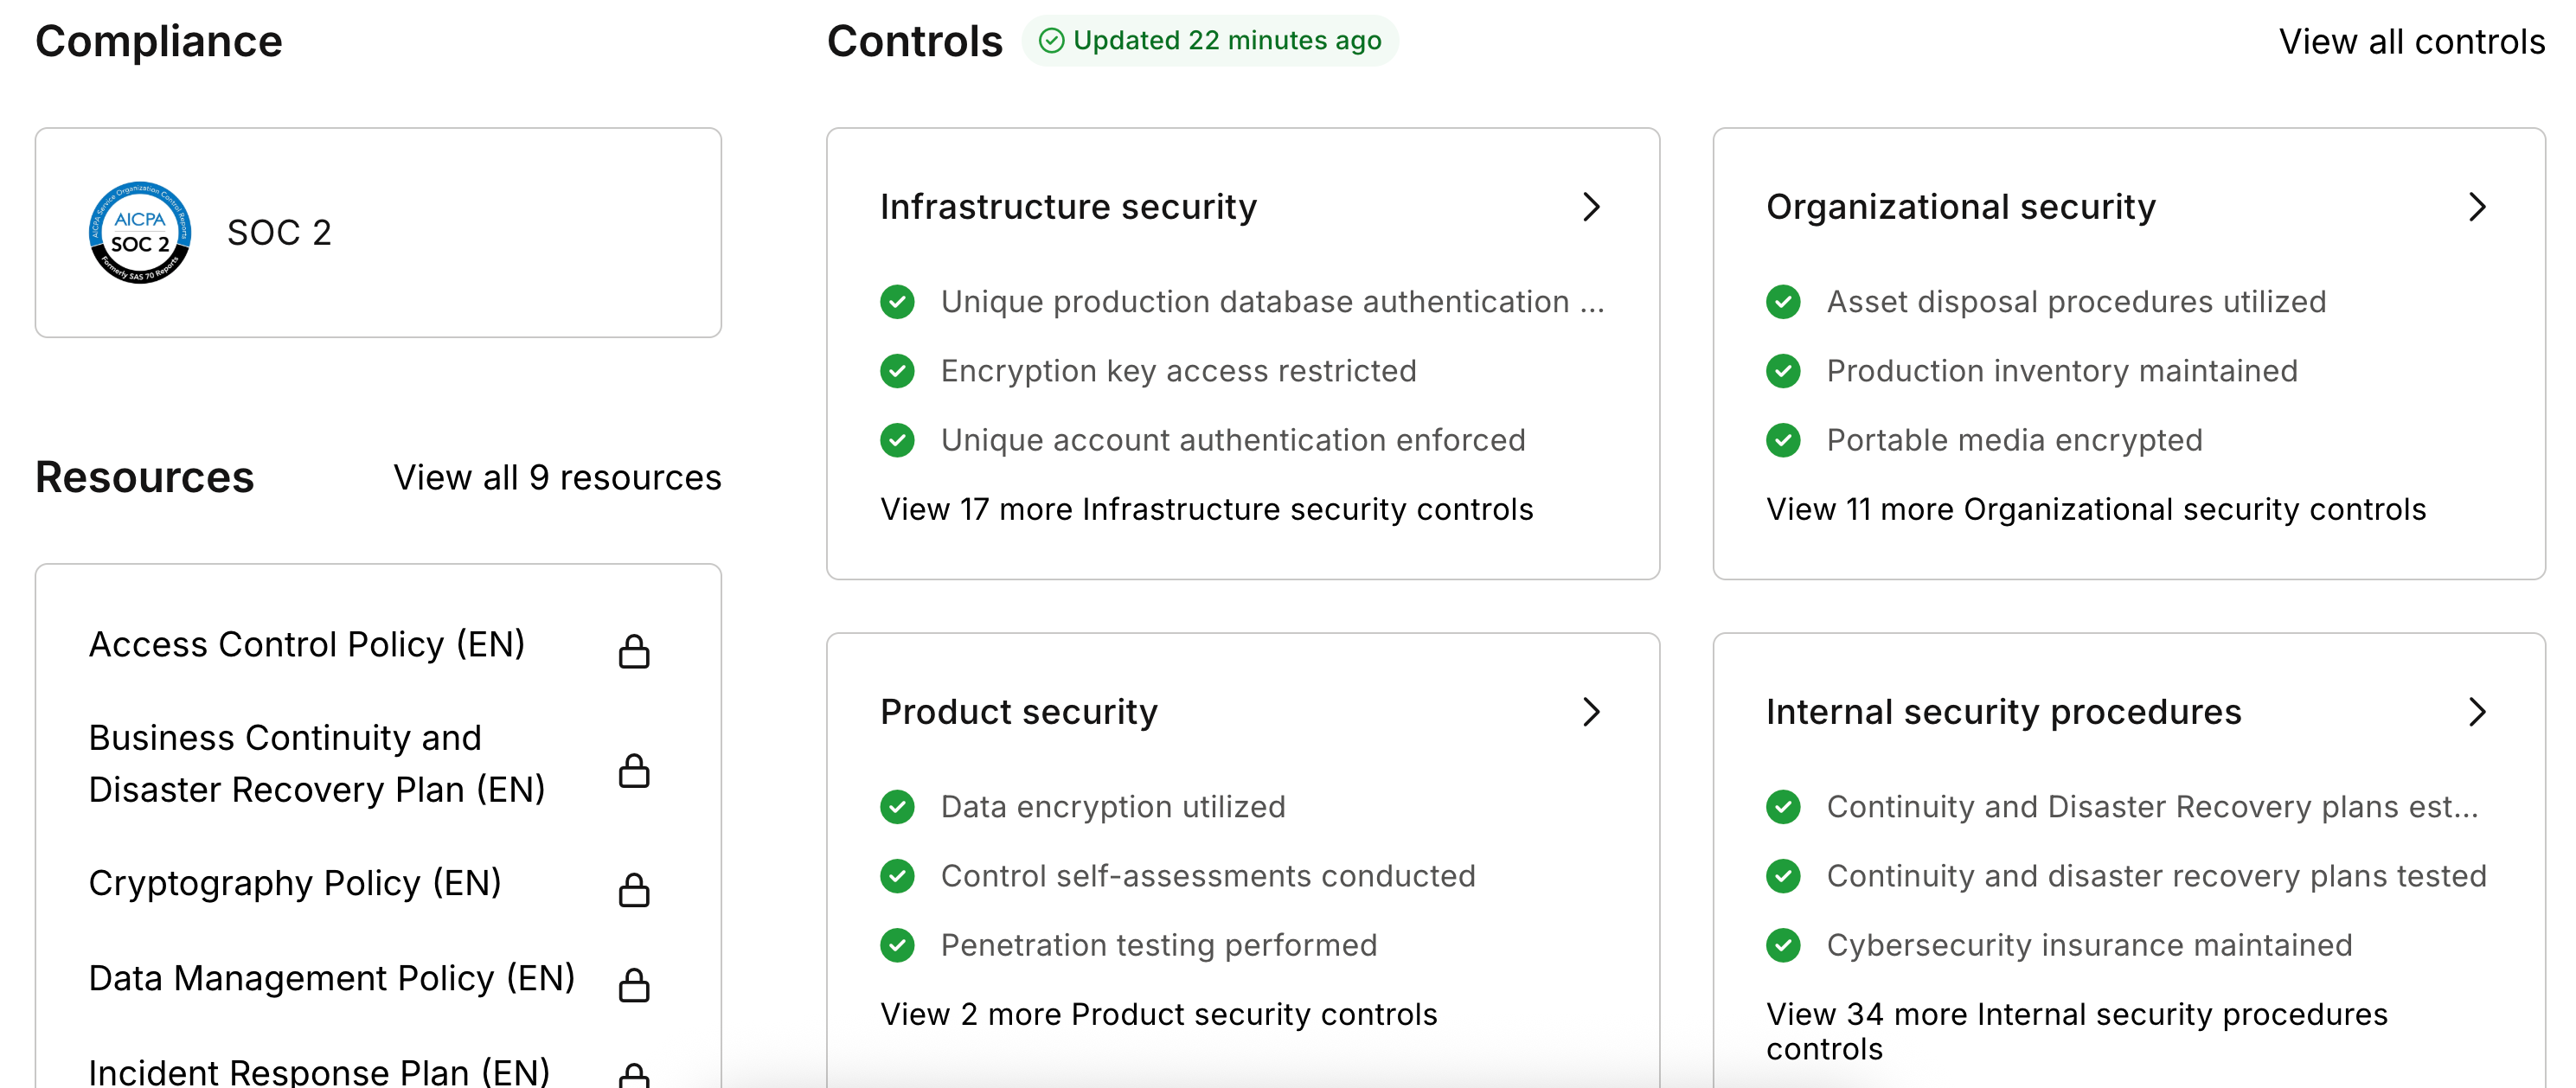
Scrunch maintains comprehensive security controls across five domains: infrastructure security, organizational practices, product safeguards, internal procedures, and data privacy protections — including compliance with the EU General Data Protection Regulation (GDPR) and the California Consumer Privacy Act (CCPA). Controls are independently verified through the SOC 2 Type II audit process and documented in the publicly accessible Scrunch Trust Center. The Trust Center is updated continuously and provides customers with real-time visibility into Scrunch's compliance posture, policy documentation, and subprocessor list.
Verify in the Scrunch Trust Center
You can independently review Scrunch’s security posture in the public Scrunch Trust Center. It provides:
- Current SOC 2 Type II audit reports and certification status
- Detailed security and data handling policies
- Information about data collection methodologies
- A complete list of third‑party subprocessors
Enterprise security features
Identity and Access Management
- Single sign-on (SSO) for Enterprise plans with Okta, Microsoft Entra ID (formerly Azure AD), and Google Workspace; supports any SAML 2.0 or OIDC‑compliant provider.
- Role-based access control (RBAC) with four defined roles — Admin, Editor, Viewer, and Guest (agency accounts only) — plus per‑brand permission controls, enabling least-privilege access enforcement across large teams.
- Options for just‑in‑time (JIT) provisioning, domain enforcement, and admin role management, reducing the risk of orphaned accounts and unauthorized access.
Regulatory Compliance
- GDPR and CCPA compliant. GDPR applies to the processing of personal data of individuals in the European Union; CCPA grants privacy rights to California residents. Scrunch's controls address both regulatory frameworks.
- Scrunch does not sell personal information to third parties.
- Data processing agreements (DPAs) are available for customers who require them under GDPR Article 28.
Platform Security and Operations
- Comprehensive audit logs of user actions, providing a tamper-evident record for compliance investigations and internal reviews.
- Secure API integrations with token‑based authentication (OAuth 2.0 bearer tokens), ensuring that data exchange between Scrunch and third-party systems is authenticated and encrypted in transit.
- Enterprise support with defined service level agreements (SLAs) and detailed analytics dashboards for monitoring platform usage and security events.
Example: implementing SSO with a SAML 2.0 provider
How to Set Up SSO on Scrunch (Step-by-Step)
- Request activation: Contact Scrunch support to enable SSO for your organization.
- Configure your identity provider: Set up the Scrunch application in your IdP (Okta, Microsoft Entra ID, Google Workspace, or any SAML 2.0/OIDC-compliant provider).
- Share IdP metadata: Provide your identity provider's metadata (XML or endpoint URLs) to Scrunch.
- Test the integration: Verify that authentication works correctly for pilot users before a broader rollout.
- Enforce SSO organization‑wide: Once confirmed, apply SSO enforcement across your entire Scrunch organization.
Step‑by‑step instructions for supported providers are available in the SSO integration guide.
Related FAQs
- Scrunch home
- Monitoring & InsightsSee how your brand shows up in AI and uncover insights to grow.
- AXPDeliver AI-optimized content to AI agents visiting your website.
- EnterpriseAI visibility, insights, and action—any scale.
- AgenciesHelp your clients navigate the AI-first customer journey.
- Guide to AI search
- Blog
- Customers
- How-to guides
- FAQs
- Prompt Generator
- Pricing
- Book a demo
- What user roles and permissions are available in Scrunch?Four user roles are available in Scrunch: Admin, Editor, Viewer, and Guest. Admins have full organizational access, Editors can create and modify content, Viewers have read-only access, and Guests (agency accounts only) see only specific brands. Permissions can be customized per brand for granular control.
- What single sign-on (SSO) providers does Scrunch support?The Scrunch Enterprise plan supports single sign-on (SSO) with major identity providers, including Okta, Microsoft Entra ID (formerly Azure AD), and Google Workspace. Any SAML 2.0 or OIDC-compliant identity provider is also supported.
- Does Scrunch collect personal information from people using AI platforms like ChatGPT?No, Scrunch doesn’t collect personal information from members of the general public as part of its service offerings.
- Customers
- About
- Terms of service
- Privacy policy
- [email protected]
- Log in
- Start free trial
- Careers
- LinkedIn
- X